01
Risk mitigation
We help clients identify risks that really matter and provide guidance to deploy controls that mitigate the potential for losses.
Cybersecurity VAR · Est. 2004
For more than twenty years, SBS Security has aligned leading security vendors with our client’s operations. Now with AI being rapidly deployed, compliance, cyber resilience, and design control are even more critical factors.
We can independently assess attack surfaces and security postures to determine how to get more value from technology - including investments already made.
Practice & Vendors
As a value-added reseller, our impact is focused on four important areas:
01Risk mitigation
02Compliance programs
03Cyber resilience
04AI integration
01
We help clients identify risks that really matter and provide guidance to deploy controls that mitigate the potential for losses.
02
Obligations are mapped to systems and to evidence. HIPAA, HITRUST, PCI-DSS, and SOC 2 are design targets for the architectures our clients are examined against. They are not badges we rent.
03
Resource identification and exposures, early detection, intelligent filtering, operational continuity and user awareness are all parts of a resilient business.
04
The agentic world changes everything - rapidly. Controlling access and retrieval of information brings new obligations in the AI universe.
Vendor alignment control matrix
| Vendor | Access | Network | Endpoint | Data | Cloud and AI | |
|---|---|---|---|---|---|---|
 | Email investigation and response | Identity investigation and response | Network alert investigation | Endpoint investigation and isolation | DLP and insider threat | Agentic SOC, cloud investigation |
 | Inbound email security | Account takeover protection | ||||
 | AI Firewall, AI-SPM, shadow AI | |||||
 | Cybersecurity asset management | |||||
 | Quantum firewall | Harmony Endpoint | CloudGuard | |||
 | Secure Email | Duo, Identity Services Engine | Secure Firewall | Secure Endpoint, XDR | Multicloud Defense | |
 | Magic WAN, Zero Trust | Cloudflare One | ||||
 | Falcon Identity | Falcon | Falcon Cloud Security | |||
 | Network detection | Endpoint detection | AI investigation | |||
 | Email security | Security Service Edge | DLP | |||
 | Managed detection and response | |||||
 | Anti-ransomware platform | |||||
 | Security awareness training | |||||
 | SIEM | |||||
 | Email security, archiving, awareness | |||||
 | Secure web gateway | DLP | SSE and CASB | |||
 | Sensitive data detection | AI data security | ||||
 | Workforce identity | |||||
 | NGFW, Prisma Access | Cortex XDR | Prisma Cloud, Prisma AIRS | |||
 | Email protection | Identity threat defense | Email DLP, insider threat | |||
 | InsightVM | InsightIDR | ||||
 | Exposure management | |||||
 | Breach and attack simulation | |||||
 | DLP | CASB | ||||
 | SIEM and SOAR | |||||
 | Data access governance | |||||
 | Email detection and response | |||||
 | Endpoint management | |||||
 | Email security | Network security | Endpoint security | |||
 | File integrity monitoring | |||||
 | Directory security | Data security platform | Data security posture | |||
 | Agentic cyber defense | |||||
 | Private Access | Internet Access | Data protection | Zero Trust Exchange |
Industries
Each engagement is customized to the specific requirements of the businesses we serve which are primarily in five sectors but often include enterprises with their own unique issues.
Operational, clinical, supplier/partner & insurer systems
Healthcare and health insurance enterprises have unique safeguard maps and face strict regulatory scrutiny, but clinical operations cannot be interrupted or impeded. SBS is particularly experienced in balancing these requirements while recognizing financial constraints.
Regulatory frameworks, access, reputation & data boundaries
Privileged access, data protection, recovery objectives, forensics and reporting authorities are all facets of a finance or insurance entity’s cybersecurity posture that require close scrutiny. With years of experience in this sector, including having a CSA in-house, SBS Security can assist clients with assuring they are functioning appropriately in this highly-regulated environment.
Customer experience, operational & supplier continuity
In the hospitality and retail world, the customer/guest experience is crucial and a hard-won reputation can come undone rapidly. The edges where patron, supplier, logistics and transaction security meet have different issues to be considered.
Campus, research, and records
A campus has many authorities: Registrar systems, research enclaves, affiliated specialty schools and clinics, and an ever-changing, often seasonal student identity that can outlive a term. Faculty, administration and student access introduce their own requirements, including keeping education records inside a boundary that can produce FERPA evidence, and isolating research data before a collaboration tool or model is allowed to see it.
IT, IoT, AI & safety
Today, in addition to all of the business security issues they've had to face over the years, cybersecurity teams are now working three problems at once.
All of these issues add to the problem of making the budget fit the solution.
In a word - GUIDANCE.
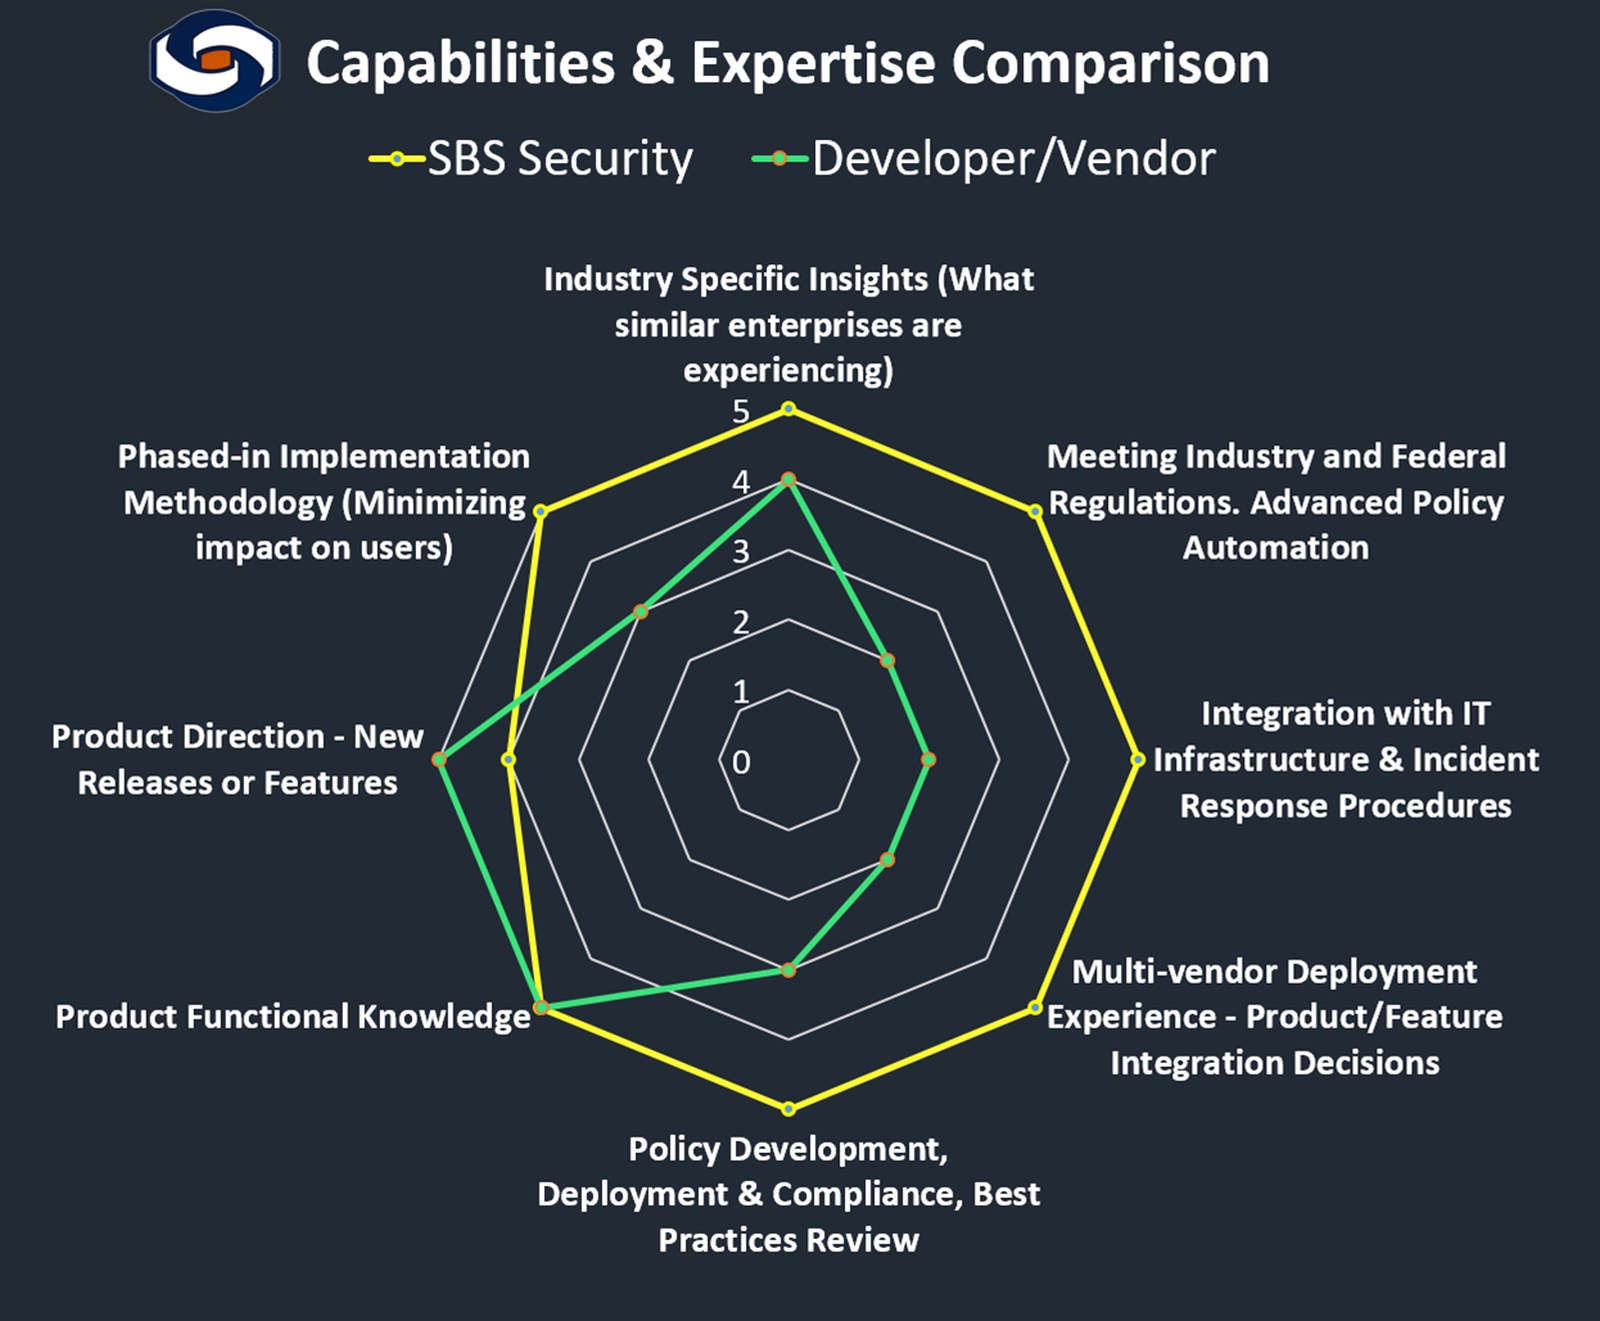
Product developer/vendors typically have only one area of capability and expertise that exceeds those of an experienced Value Added Reseller like SBS – and that is limited to their internal and proprietary new product planning, development and release scheduling.
In all other facets of successful product selection, integration, and operation, that guidance is what SBS provides.
We understand the pressure: too many tools, not enough people, and a threat landscape that now includes email, endpoints, SaaS, and AI. There is a better way than buying another product and hoping it sticks.
Sound decisions. Stronger protection. That's who we are.
For regulated entities, our technology and product approaches are mapped to the obligations our clients are faced with.
HIPAA is federal law administered by the U.S. Department of Health and Human Services. The Office for Civil Rights enforces the Privacy, Security, and Breach Notification Rules that govern protected health information. HHS does not issue a HIPAA certificate.
HITRUST CSF certification is issued by HITRUST, a private organization. The framework maps controls used by healthcare and other regulated businesses, and assessors report results to HITRUST for certification.
The Payment Card Industry Data Security Standard is maintained by the PCI Security Standards Council, founded by the card brands. Compliance is assessed against the council’s standard for environments that store, process, or transmit cardholder data.
SOC 2 reports are issued by independent CPAs under standards from the American Institute of CPAs. The examination uses the Trust Services Criteria for security, availability, processing integrity, confidentiality, and privacy.
Request a briefing
Provide your name, company, contact info and industry as well as what you'd like to achieve from the briefing. Please provide some dates and times we could initially reach you to discuss the schedule for the briefing.